What is a cookie on a website? Whether you are a website owner or an internet user, you have probably encountered cookies before. But what exactly are they?
Simply put, cookies are small pieces of data that websites can ask your browser to store on your device. They can help a website recognise a session, remember preferences and customise the browsing experience. Cookies support many useful website functions. For example, they can keep products in a shopping cart, remember a language preference or maintain a secure login session.
However, websites can also use cookies for analytics, profiling and advertising. That distinction matters. A cookie is not automatically necessary, harmless or privacy-friendly simply because a website uses it.
What is a cookie and what do cookies do?
HTTP cookies, also known as web cookies, are small pieces of information that a website asks your browser to store on your device.
When you visit a website, your browser sends a request to a web server. The website may respond by sending a cookie to your browser. During a later request or visit, your browser can send that cookie back to the relevant website.
This allows the website to recognise an existing session or retrieve information associated with it. Cookies can store or reference information such as:
- Language and regional preferences
- Session identifiers
- Login status
- Shopping-cart identifiers
- Consent choices
- Analytics identifiers
- Advertising identifiers
Websites use cookies for purposes including session management, personalisation, analytics and advertising.
However, the cookie does not always contain the information itself. For example, a shopping-cart cookie may contain only a random identifier. The website then uses that identifier to retrieve the contents of the shopping cart from its server.
Cookies can help websites remember users and support useful features. However, cookies used for tracking or profiling can create privacy risks, particularly when organisations follow users across websites or combine cookie identifiers with other information.
Well-designed websites should avoid storing sensitive information directly in cookies. They should also protect session identifiers and similar data against unauthorised access.
Different types of cookies
Cookies can be classified in different ways. A cookie’s purpose describes why the website uses it. Its provider describes which website or service sets or receives it. Its duration describes how long it remains available.
As a result, the same cookie can be first-party, persistent and used for analytics at the same time.
|
Classification |
Common categories |
What it describes |
|
Purpose |
Necessary, functional, analytics, advertising |
Why the cookie is used |
|
Provider |
First-party, third-party |
Which website or service sets or receives it |
|
Duration |
Session, persistent |
How long the cookie remains available |
These classifications overlap. Labels such as first-party, third-party, session or persistent do not by themselves determine whether a cookie is necessary or whether consent is required.
Strictly necessary cookies
Strictly necessary cookies support functions that a website needs to provide a service explicitly requested by the user. Examples may include cookies used for:
- Maintaining a secure login session
- Remembering products in a shopping cart
- Protecting forms against fraud or abuse
- Distributing traffic between servers
- Processing an online transaction
- Storing a user’s cookie preferences
A cookie does not become strictly necessary simply because it is useful to the website owner. For example, a shopping-cart cookie may be necessary to complete an online purchase. An advertising cookie placed on the same website is not necessary for that purchase.
Strictly necessary cookies may still contain or refer to identifiers. Website owners must therefore protect them appropriately and explain their purpose clearly.
Functional cookies
Functional cookies support additional website features and preferences.
They may remember:
- A preferred language
- A selected region
- Accessibility settings
- Display preferences
- Video-player settings
- Previous support or chat choices
These cookies can make a website more convenient and personal.
However, functional cookies are not automatically strictly necessary. Depending on their purpose, implementation and the applicable law, some functional cookies may require consent.
Analytics and performance cookies
Analytics and performance cookies help organisations understand how visitors use a website. They may measure:
- Page views
- Navigation paths
- Traffic sources
- Interactions with buttons and forms
- Technical errors
- Page performance
- Completed transactions or conversions
Organisations can use this information to identify broken pages, confusing navigation and technical problems.
However, analytics cookies are not automatically anonymous. An analytics service may collect or generate identifiers, device details, IP-related information and behavioural data. In many European jurisdictions, analytics cookies require prior consent. Some national regulators provide limited exceptions for carefully configured, privacy-friendly analytics. However, those exceptions depend on local requirements and the actual configuration of the technology.
Website owners should therefore assess how an analytics tool behaves rather than relying only on the label “analytics”.
First-party cookies
First-party cookies are associated with the website a user is currently visiting.
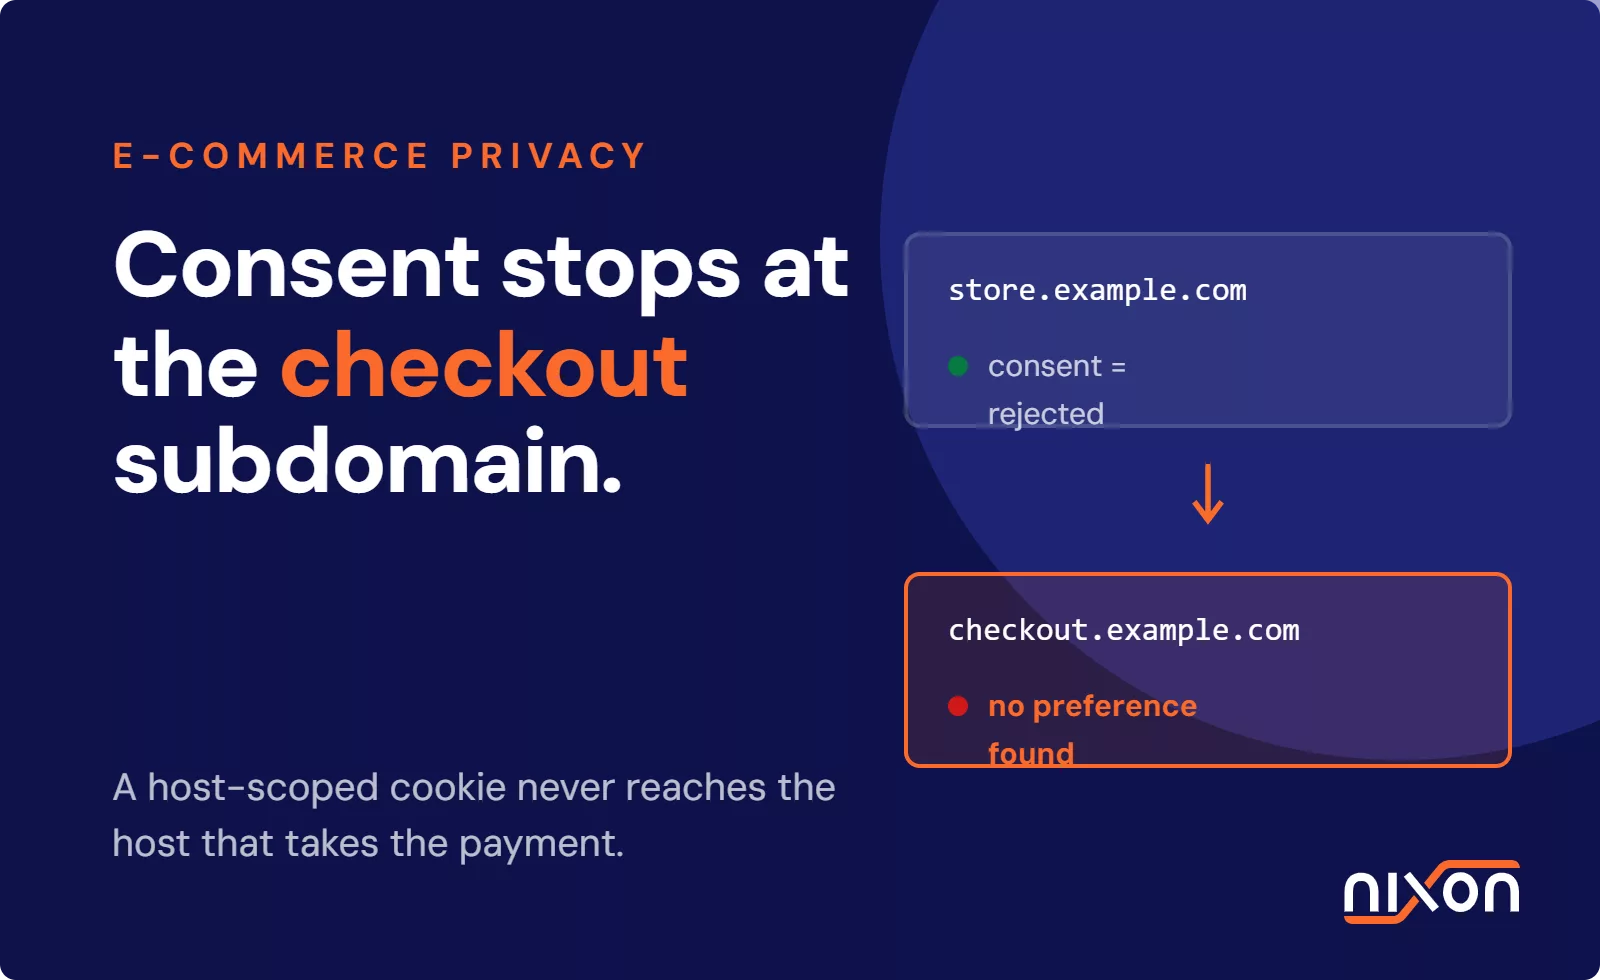
For example, when someone visits example.com, a cookie associated with example.com is generally considered a first-party cookie.
Websites can use first-party cookies for:
- Login sessions
- Shopping carts
- Language preferences
- Consent settings
- Analytics
- Personalisation
- Conversion measurement
- Advertising
First-party only describes which website sets or receives the cookie. It does not mean that the cookie is automatically necessary, harmless or exempt from consent requirements.
A first-party analytics or advertising cookie may still require consent.
Session cookies
Session cookies are temporary cookies designed to remain available during a browsing session.
Websites commonly use them for:
- Authentication
- Shopping carts
- Navigation
- Security
- Multi-step forms
A session usually begins when a user opens a website or web application. It ends when the user logs out, closes the browser or otherwise ends the session.
The browser normally removes session cookies when the session ends. However, exact behaviour can vary because some browsers can restore previous sessions.
Non-necessary cookies
Non-necessary, or non-essential, cookies are not required to provide the basic service requested by the user.
They commonly support:
- Optional personalisation
- Audience measurement
- Advertising
- Retargeting
- Social-media integrations
- Embedded third-party content
When consent is required, these cookies and the technologies that place or access them should remain inactive until the user has made a valid choice.
Rejecting non-essential cookies should not prevent the user from accessing website features that do not depend on those cookies.
Targeting and advertising cookies
Targeting and advertising cookies help organisations deliver, personalise and measure advertising.
They may be used to:
- Build audience profiles
- Display personalised advertisements
- Retarget previous website visitors
- Limit how often an advertisement appears
- Measure advertising conversions
- Connect activity across websites or services
- Analyse the performance of advertising campaigns
These cookies may collect information about pages viewed, links clicked, products considered and interactions with advertisements.
Targeting and advertising cookies usually require prior consent. They should not activate while the user is still deciding whether to accept or reject them.
Advertising technologies do not always rely only on cookies. They can also use pixels, scripts, local storage, server-side identifiers and other techniques.
Third-party cookies
Third-party cookies are associated with a domain or service other than the website the user is currently visiting.
A website may include third-party services for:
- Embedded videos
- Payment processing
- Customer-support tools
- Social-media content
- Fraud prevention
- Analytics
- Advertising
- Audience measurement
Not every third-party cookie is used for advertising. A payment provider, embedded video service or fraud-prevention tool may also place a third-party cookie.
However, third-party tracking can create significant privacy risks when it allows organisations to follow users across different websites or combine information from multiple sources.
Many browsers restrict third-party cookies in certain circumstances. The exact behaviour depends on the browser, user settings, browsing mode and technical implementation.
Persistent cookies
Persistent cookies remain stored after the user ends the current browsing session.
They remain available until:
- Their configured expiry date passes
- The website replaces or removes them
- The user deletes them
- The browser or device clears them
Persistent cookies can remember preferences across visits. They can also support longer-term analytics, profiling and advertising.
A persistent cookie should not remain stored longer than necessary for its stated purpose. Website owners should therefore review both its purpose and its configured retention period.
Zombie cookies
The term “zombie cookie” describes tracking information that is recreated after a user has deleted it.
For example, a service may use another storage mechanism to restore a deleted identifier. As a result, the identifier appears to return without the user actively accepting it again.
This practice can undermine user choice and create serious privacy and compliance concerns. A user who deletes or rejects tracking technologies should not have those identifiers secretly restored through another method.
Benefits of cookies
Cookies are not inherently bad. When organisations use them proportionately and securely, they can make websites safer, more useful and easier to navigate.
They optimise session management.
HTTP requests do not automatically remember previous interactions. Cookies allow a website to connect multiple requests to the same session.
As a result, users can:
- Remain logged in
- Move between checkout pages
- Keep products in a shopping cart
- Complete multi-step forms
- Use secure account features
- Return to an unfinished process
The website does not necessarily store all this information inside the cookie. Instead, the cookie can contain a random identifier that connects the browser to information stored securely on the server.
They allow for a more personal experience
Cookies can prevent users from having to select the same settings during every visit.
For example, a website may remember:
- Language
- Region
- Currency
- Accessibility preferences
- Display settings
- Privacy choices
E-commerce websites can also use cookies to retain products in a shopping cart or remember recently viewed items.
Advertising technologies may use cookies and related identifiers to personalise or measure advertisements. However, where this involves non-essential tracking or profiling, the website may first need the user’s consent.
Dangers of cookies
Cookies cannot execute programs or directly infect a device with malware. Nevertheless, their use can create privacy and security risks.
Tracking and profiling
Tracking cookies can record behaviour over time. When organisations combine cookie identifiers with browsing history, account information or other data, they may infer a person’s:
- Interests
- Habits
- Purchases
- Preferences
- Location
- Likely future behaviour
Cross-site tracking can be particularly intrusive because it follows users beyond a single website.
Session hijacking
When a user logs in, a website may place a session cookie in the browser. This cookie helps the website recognise that the user has already authenticated.
If an attacker obtains a valid session identifier, the attacker may be able to impersonate the user. Depending on the service, this could provide unauthorised access to:
- Online accounts
- Personal information
- Company systems
- Purchases or payments
- Confidential documents
Website owners can reduce this risk by using HTTPS, limiting cookie lifetimes and applying appropriate security attributes. For example:
Securelimits the cookie to encrypted HTTPS connections.HttpOnlyhelps prevent JavaScript from reading the cookie.SameSitecontrols whether the browser sends the cookie in certain cross-site situations.
These controls reduce risk, but they do not replace secure website development and proper access controls.
Excessive or unknown data collection
A website may use more cookies and trackers than its owner realises. This often happens when teams add:
- Marketing tags
- WordPress plugins
- Embedded videos
- Chat tools
- Advertising pixels
- A/B-testing software
- New campaign technologies
Over time, technologies can remain active even after the organisation has stopped using them.
A consent-management platform may only control technologies that have been identified and configured correctly. Hard-coded scripts or newly introduced plugins may operate outside that configuration.
Website owners should therefore test what their live website actually does rather than relying only on the settings shown inside their consent-management platform.
The future of cookies
The web is likely to become more privacy-conscious, but it will not become completely cookieless. First-party cookies will continue to support important functions such as:
- Authentication
- Security
- Shopping carts
- Consent preferences
- Language settings
- Session management
At the same time, browsers, regulators and users are placing greater restrictions on cross-site tracking.
As a result, organisations should reduce unnecessary tracking and collect only the information they genuinely need. They can also explore approaches such as contextual advertising, aggregated measurement and privacy-preserving analytics.
However, replacing a cookie with another identifier does not automatically improve privacy. Technologies such as fingerprinting, link decoration and hidden server-side matching can be even less transparent because users may struggle to detect or control them.
The better approach is not to find a new way to follow every user. Instead, organisations should understand which information they genuinely need and design their websites accordingly.
Cookies and GDPR
Cookies are not automatically personal data. However, a cookie identifier can become personal data when an organisation can connect it to an identifiable person, account, device or profile.
The GDPR recognises that cookie identifiers and other online identifiers can leave traces. When organisations combine those traces with unique identifiers or other information, they may use them to identify people or create profiles.
When cookie use involves personal data, organisations must comply with GDPR principles such as:
- Lawfulness, fairness and transparency
- Purpose limitation
- Data minimisation
- Storage limitation
- Security
- Accountability
In addition, European ePrivacy rules generally require consent before a website stores information on a user’s device or accesses information already stored there. Limited exceptions apply when the storage or access is:
- Used solely to transmit a communication over an electronic communications network; or
- Strictly necessary to provide a service explicitly requested by the user.
This means that the ePrivacy rules can apply even when the information stored in a cookie is not personal data.
A legitimate interest under the GDPR does not automatically allow an organisation to place or access non-essential cookies. The organisation must first comply with the applicable ePrivacy requirements.
Because national laws and regulator guidance can differ, organisations operating in multiple countries should also consider the requirements in each relevant market.
To comply with the GDPR and applicable ePrivacy requirements, website owners should:
- <>Obtain consent before placing or accessing non-essential cookies and similar technologies.
- Explain clearly which technologies are used, what information they collect and why they are used.
- Record consent choices appropriately and retain evidence of the relevant consent configuration.
- Keep optional technologies inactive when a user rejects them.
- Avoid making optional cookies a condition for using services that do not require them.
- Make withdrawing consent as easy as giving it.
- Keep the cookie notice aligned with the behaviour of the live website.
- Repeat testing after website releases, campaign launches and technology changes.
A cookie banner alone does not prove that a website complies. The banner must also control the relevant technologies correctly.
In conclusion, what is a cookie on a website?
A cookie on a website is a small piece of data that helps a browser and website remember information between requests or visits.
Some cookies provide essential functions, such as maintaining a secure login session or remembering a shopping cart. Others support personalisation, analytics or advertising.
You can classify cookies according to their purpose, provider and duration. These classifications can overlap. Website owners should therefore not assess a cookie based only on labels such as first-party, third-party, session or persistent.
Instead, they should examine:
- Why the cookie is used
- What information it contains or refers to
- Which parties receive the information
- How long the cookie remains stored
- Whether consent is required
- Whether the live website respects the user’s choice
Used carefully, cookies can make websites secure and convenient. Used without transparency, proper consent or appropriate safeguards, they can create privacy and security risks.
For website owners, the most important question is not simply whether the website uses cookies. The more important question is whether every cookie and related technology behaves in line with the user’s choice.
How does Nixon Digital help you comply?
Managing cookie compliance across one or more websites can be challenging. Website teams regularly add new pages, plugins, campaigns and third-party services. As a result, the technologies used by the live website can change without the privacy or compliance team noticing.
A consent-management platform can help control known technologies. However, it does not automatically prove that every script, cookie and tracker follows the configured consent rules.
Hard-coded scripts, incorrectly categorised technologies and newly introduced plugins may still activate outside the consent-management platform.
Nixon Pro scans websites across multiple pages and helps organisations identify cookies, third parties and privacy risks that require further investigation.
A Nixon Pro scan can help organisations answer questions such as:
- Which cookies and third parties are active on the website?
- Do non-essential technologies activate before consent?
- Does the live website match the cookie notice?
- Do accept and reject choices work as intended?
- Have new website releases introduced unexpected technologies?
- Do privacy issues appear only on specific pages?
Recurring scans also help teams verify that their website continues to behave as intended after changes and releases.
What is a cookie on a website?
What do cookies do?
What are cookies used for?
The four most common uses are session management (logins, shopping carts), preferences (language, region, dark mode), analytics (measuring traffic and behavior) and advertising (targeting and retargeting). The first two are usually first-party cookies set by the website itself. The last two are often third-party cookies set by external companies whose scripts run on the page.
What are the types of cookies?
By origin, cookies are first-party (set by the website you are visiting) or third-party (set by another domain whose script the website loads). By duration, they are session cookies (deleted when you close the browser) or persistent cookies (stored for a set period). By purpose, GDPR groups them as strictly necessary, functional, analytics or marketing. Only strictly necessary cookies are exempt from consent.
Are cookies safe?
Cookies themselves cannot carry viruses or run code. The risk is in what is stored in them and who can read them. A cookie containing a session token can be stolen if a website is not properly secured over HTTPS. Third-party tracking cookies are not dangerous in the malware sense, but they can expose your browsing behavior to companies you never directly interacted with.
How long do cookies last?
Can I delete cookies?
Do all websites use cookies?
Want to be absolutely sure that your website is compliant?
Want to be absolutely sure that your website is compliant?
Check your website for GDPR or CCPA violations. Gain insight into the behavior of third-party cookies, trackers, domains, and fonts.
- Ready within 2 minutes
- Built for GDPR
- Know if you are compliant