Total GDPR fines exceeded €7.1 billion since May 2018. Over 60 percent of that total was issued after January 2023. Enforcement is accelerating, not plateauing.
That acceleration matters. For compliance officers, data protection officers, and executives building privacy infrastructure, the fines data reveals where regulators are focusing their resources. It shows which Articles are generating the largest penalties. It identifies which sectors are under the heaviest scrutiny. Most importantly, it tells you what you need to fix first.
The Scale of GDPR Enforcement: A Data View
According to enforcementtracker.com and the European Data Protection Board’s annual reports, regulators have issued GDPR fines across more than 1,400 decisions as of early 2026. The €7.1 billion figure represents the cumulative administrative penalty across all EU member states, the UK and partner jurisdictions.
But the distribution of that money matters more than the total. Between May 2018 and December 2022, roughly 40 percent of all GDPR fines were issued. Between January 2023 and March 2026, regulators issued more fines than in the preceding five years combined. This is not a plateau. This is a ramp.
The acceleration reflects three factors: regulators developing institutional expertise, DPAs staffing up after initial hiring and organizations that ignored GDPR compliance finally reaching enforcement action. The learning curve is over. The enforcement machinery is running.
Where the Money Is: Article Violations by Category
GDPR enforcement does not distribute evenly across the regulation. Four primary violation categories account for roughly 94 percent of all fines:
Unlawful Processing (Article 6): 34 percent of total fines. This category covers insufficient legal basis for processing, weak consent mechanisms and failure to establish lawful processing grounds. It remains the single largest source of enforcement action.
Insufficient Technical and Organizational Measures (Articles 25 and 32): 28 percent. These fines target inadequate security controls, missing data protection impact assessments and failure to implement privacy by design. They often increase in severity when combined with data breaches.
Transparency Failures (Articles 13 and 14): 22 percent. Regulators fine organizations for incomplete or inaccurate privacy notices, missing disclosures about data retention, inadequate information about data subject rights and opacity around automated decision-making.
Data Subject Rights Violations (Articles 15-22): 16 percent. These fines address failure to fulfill access requests, deletion requests, portability claims, or objections to processing within required timelines.
The remaining six percent covers other violations, including breaches of Article 5 principles, failure to notify regulators of data breaches and misuse of data protection officer appointment requirements.
Understanding this distribution is critical. If your organization’s compliance focus emphasizes security frameworks while neglecting consent documentation, your risk profile misaligns with where regulators are writing checks.
2025-2026: Four Emerging Trends
1. Consent-Based Fines Are Increasing
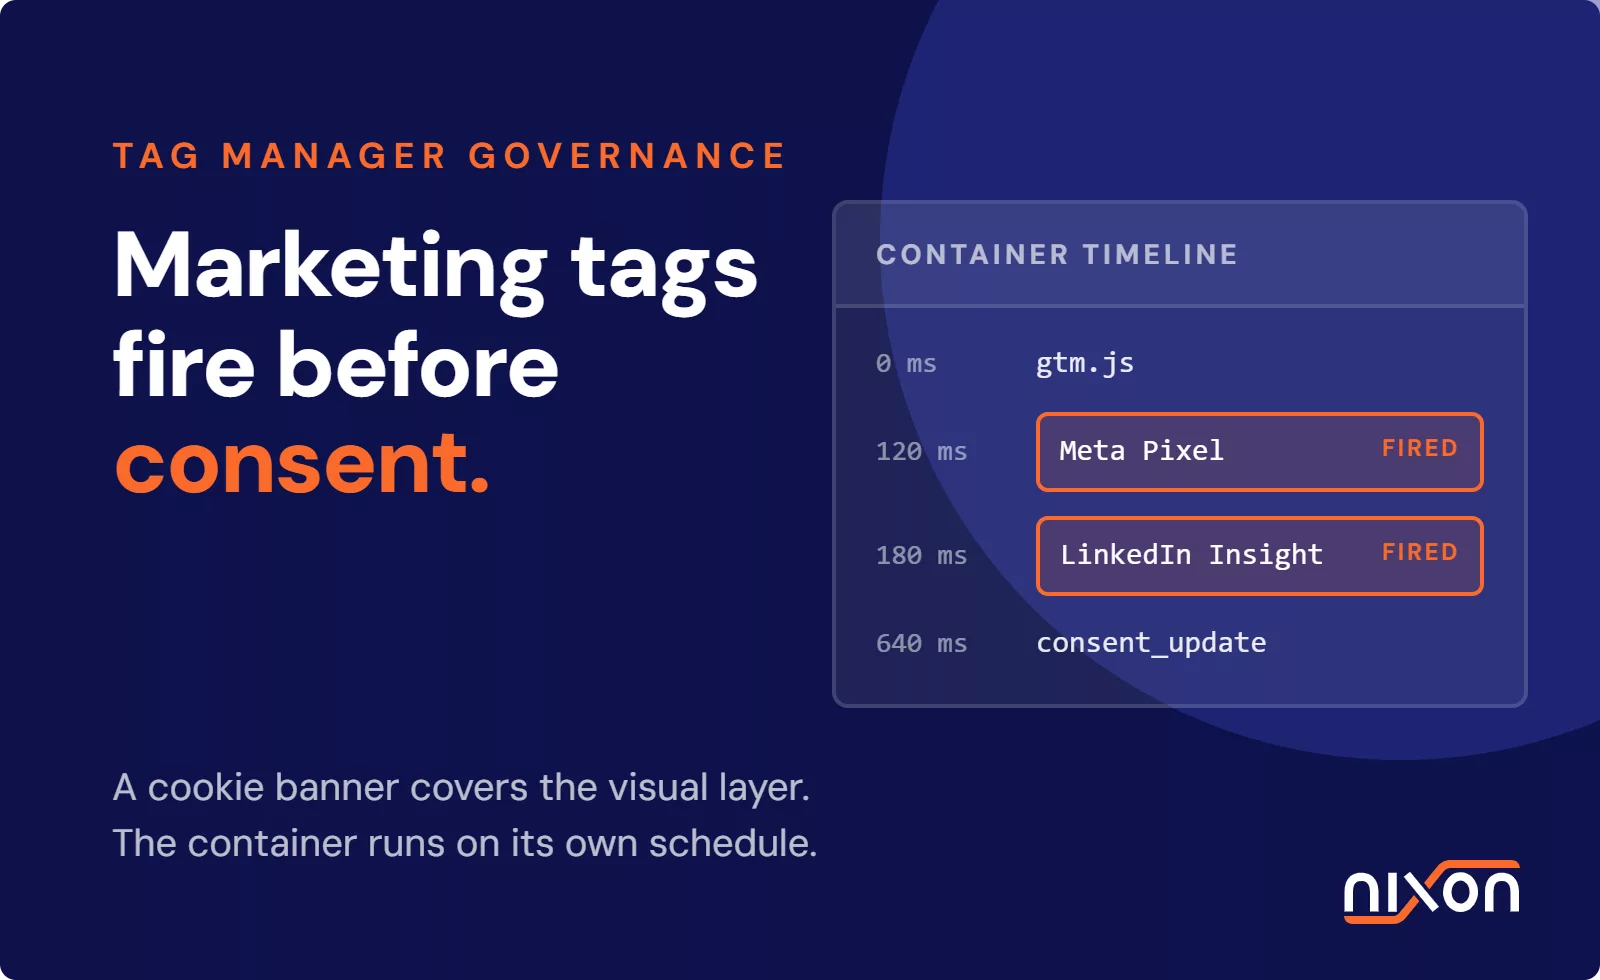
Website tracking and cookie compliance failures now account for a measurable spike in enforcement action. Regulators across multiple jurisdictions have shifted focus toward consent mechanisms on company websites. Data from enforcement trackers shows consent-related fines have grown substantially year-over-year since 2023. The trend continues into 2026.
Organizations often treat cookie policies as legal compliance theater: add a banner, collect checkbox evidence, move on. Regulators see differently. They examine whether consent is freely given, specific, informed, and unambiguous. Dark patterns that bury opt-outs in secondary clicks, pre-ticked boxes that default to agreement and consent requests framed as non-negotiable gates all trigger enforcement action.
2. Cross-Border Coordination is Becoming Standard
The European Data Protection Board’s enforcement coordination efforts have moved beyond guidance documents into active cooperative investigations. When a large organization or platform operates across five or more EU jurisdictions, regulators now coordinate their examinations and enforcement timelines. This dramatically increases the speed of resolution and the size of penalties.
A single violation that might have drawn €2 million in enforcement action from one national DPA now draws coordinated fines from multiple regulators, reaching €15-25 million across jurisdictions. The coordination model is becoming the default approach for multiregional cases.
3. SMEs Are Not Exempt
A persistent misconception holds that GDPR enforcement targets only large enterprises. Enforcement tracker data contradicts this assumption. A significant share of all GDPR fines are issued to smaller organizations: regional service providers, local agencies and small SaaS companies.
SMEs face lower absolute penalties, but they face penalties nonetheless. The difference is that enterprise enforcement generates larger headlines. Regulators treat smaller organizations with proportional severity, not exemption.
4. Transparency Enforcement Is Expected to Spike in H2 2026
The EDPB’s 2026 calendar includes a coordinated enforcement action focused on transparency compliance. This initiative will examine privacy notices, consent documentation, data subject communication clarity and disclosure accuracy across multiple sectors and jurisdictions. Historical coordinated actions have consistently resulted in a spike in related fines within 6-12 months of announcement.
Organizations that conduct audit of their transparency materials now face a six-month window to remediate gaps before coordinated enforcement activity reaches full intensity.
Sectoral Pressure: Who Gets Fined Most
Enforcement pressure varies across sectors. Telecom and broadcasting organizations account for the highest cumulative fine amounts, driven by a small number of large penalties for customer data mishandling. Healthcare and public sector organizations face the highest fines per capita, proportional to their organizational size.
Growth areas include fintech and online platforms. Since 2023, fines issued to fintech organizations have grown substantially. Payment processors, lending platforms, and digital asset exchanges face intensifying scrutiny around consent, legal basis documentation and customer data access rights.
Public sector enforcement is also growing. Educational institutions, government agencies, and publicly owned utilities increasingly face GDPR fines. This represents a shift from early-period enforcement, which concentrated on private sector organizations.
What Organizations Need to Do Now
The fines data points to four priority areas for compliance investment:
First: Document your legal basis for processing. Article 6 violations account for one-third of all enforcement action. Your documentation cannot be retrospective. It must precede data collection. For every dataset your organization maintains, you need documented legal basis, and that documentation needs to be evidence of contemporaneous thinking, not post-hoc justification.
Second: Audit your consent mechanisms. If your website uses cookie banners or consent requests, test them. Examine whether consent is truly freely given, truly specific, and truly informed. If your consent design includes dark patterns, fix it immediately. These are exactly where regulators are directing resources in 2026.
Third: Implement accurate, specific privacy disclosures. Your privacy policy should disclose specific retention periods, not generic timeframes. It should explain automated decision-making with clarity. It should disclose data sharing with specificity, not broad categories. Vague transparency is regulators’ second-largest target.
Fourth: Monitor your documentation at scale. Use compliance monitoring tools to track consent implementation, privacy notice accuracy and legal basis documentation across your organization. Manual audits do not scale.
Nixon Platform provides continuous monitoring of your website portfolio – tracking consent behavior, detecting new third-party scripts, and alerting you when something changes. For website-specific compliance scanning, Nixon Pro identifies pre-consent tracking, consent mechanism failures and transparency gaps that regulators target.
Additionally, the EDPB’s coordinated enforcement trajectory makes this an urgent moment to examine your transparency materials. Our EDPB transparency enforcement analysis breaks down the specific compliance areas under review in 2026’s coordinated action.
The Bottom Line
GDPR enforcement is not slowing. It is not becoming more lenient. It is becoming faster, more coordinated and increasingly focused on transparency and consent documentation. The €7.1 billion in fines issued to date represents just the first phase of enforcement maturity.
Organizations that treat GDPR as a box-checking exercise will find themselves on the wrong side of that enforcement trend. Those that treat GDPR as a data governance practice, with documented processes, audit trails, and continuous monitoring, are already building the infrastructure regulators expect to see.
The fines data tells you exactly where to start.
Related reading: EDPB 2026 enforcement focus: transparency requirements | Cookie banner audit: does your banner actually work? | GDPR privacy policy requirements
Frequently Asked Questions (FAQ)
How much has been fined under GDPR so far?
Total GDPR fines have exceeded €7.1 billion since May 2018. More than 60 percent of that total was issued after January 2023 alone. Enforcement is not slowing down – regulators are becoming faster, better staffed, and increasingly coordinated across EU jurisdictions.
Which GDPR violations result in the largest fines?
Four categories account for roughly 94 percent of all penalties. Unlawful processing (Article 6) leads at 34 percent, followed by insufficient technical and organizational measures (28 percent), transparency failures in privacy notices (22 percent), and violations of data subject rights (16 percent). If your compliance focus is mainly on security while neglecting consent documentation, your risk profile is misaligned with where regulators are actually issuing fines.
Do smaller organizations really get fined under GDPR?
Yes. A common misconception is that GDPR enforcement only targets large enterprises. Enforcement data shows that a significant share of all fines are issued to smaller organizations – regional service providers, local agencies and small SaaS companies. The absolute amounts are lower, but the enforcement is real. Regulators apply proportional severity, not exemption.
What is changing about cookie banner compliance in 2026?
Regulators are shifting attention toward whether consent mechanisms actually work – not just whether a banner is present. They examine if consent is freely given, specific, and informed. Dark patterns like buried opt-outs, pre-ticked boxes, and consent framed as a non-negotiable gate all trigger enforcement action. Consent-related fines have grown substantially year-over-year since 2023 and the trend continues into 2026.
Why is 2026 an urgent moment to review privacy disclosures?
The EDPB has announced a coordinated enforcement action for the second half of 2026 focused specifically on transparency – privacy notices, consent documentation, and disclosure accuracy. Based on historical patterns, coordinated actions consistently result in a spike in related fines within 6 to 12 months of announcement. Organizations have roughly a six-month window now to identify and fix gaps before enforcement activity reaches full intensity.