Privacy by design for websites means a legal policy alone cannot stop a third-party marketing tag from harvesting form inputs before a user gives consent. True privacy requires web developers to enforce strict consent logic at the architecture level. A surface-level banner is not enough. For frontend and engineering teams, this means translating regulatory obligations into technical specifications. They must build web applications that default to zero data collection. This guide shows engineering teams how to implement Data Protection by Design directly into their codebase and script management pipelines.
Why privacy by design is a frontend engineering discipline
Website privacy compliance is a technical architecture problem, not just a legal one. Privacy policies and cookie notices are necessary. However, they are meaningless if the website’s code does not respect a user’s choices. Frontend engineering is therefore the primary discipline for ensuring compliance.
Moving past legal checklists to code architecture
The GDPR codifies this concept in its Article 25 text, which mandates “Data Protection by Design and by Default.” The law requires organizations to implement technical and organizational measures to safeguard data protection principles. The EDPB Guidelines 4/2019 on Data Protection by Design and by Default clarify this is not a one-time exercise. Teams must bake privacy considerations into the entire development lifecycle, from design to deployment and maintenance.
The technical failure of surface level consent banners
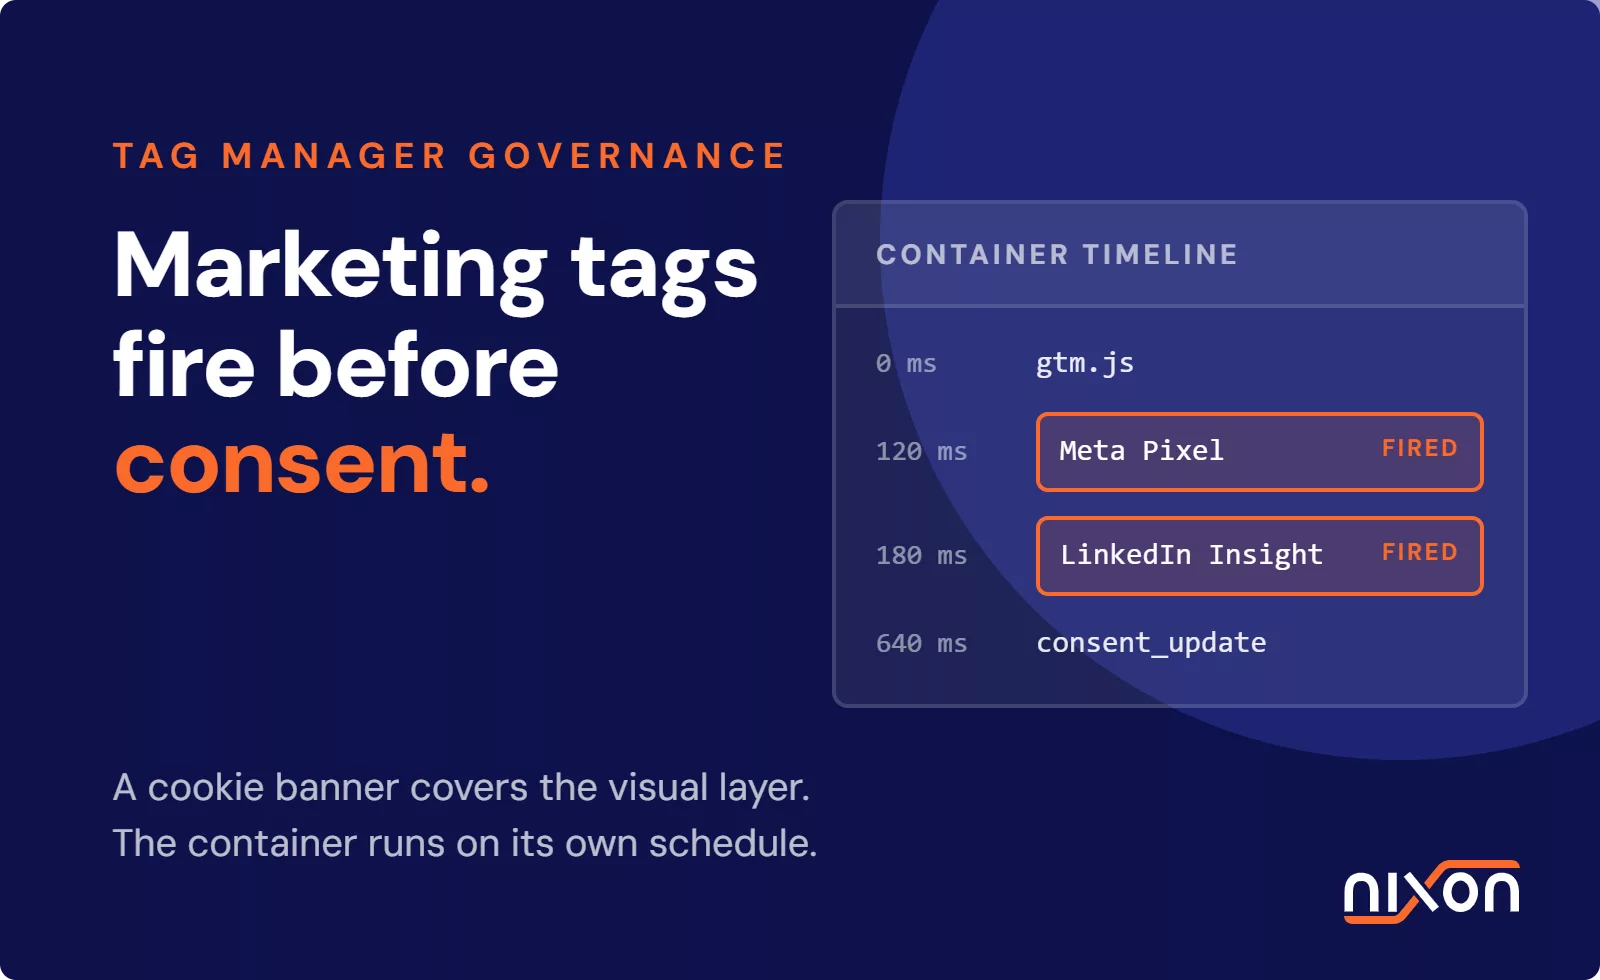
Many websites use consent banners that act as a simple overlay. This gives a false sense of security. The technical reality is that a tag manager often loads third-party scripts, like those for analytics or advertising, asynchronously. These scripts can execute and send data the moment the page starts loading. This often happens before the consent management platform (CMP) script has initialized. This race condition means trackers can collect user data before the visitor has given or denied consent, which directly violates GDPR principles.
What are the core frontend patterns for privacy by design?
To move beyond failing overlays, development teams must adopt architectural patterns that enforce consent at the code level. These strategies ensure the website collects no data without an explicit legal basis and user action. Core patterns include:
- Zero trust tag management: Block all scripts by default and only allow them to execute with explicit user consent.
- Zero PII data layer patterns: Prevent personally identifiable information from ever entering the client-side data layer.
- Self-hosting third-party dependencies: Serve assets like fonts and libraries from your own domain to avoid data sharing with external parties.
Zero trust tag management
A zero-trust approach to tag management assumes no third-party script runs by default. Instead of trying to block a list of “bad” tags, you block everything. Tags can only fire when the CMP confirms that the user provided explicit consent for that specific purpose category. The CMP typically manages this through custom events it pushes to the data layer. These events then act as triggers in your tag management system. This model is safer because it blocks newly added scripts automatically until someone correctly configures them for consent.
Zero PII data layer patterns
The data layer (window.dataLayer) is a common source of data leakage. Development teams might inadvertently push Personally Identifiable Information, such as email addresses or names from a form submission, into the data layer. They do this to track conversions. Analytics and marketing tags then sweep up this data and send it to third-party vendors. This is a clear compliance violation. A privacy-first pattern involves sanitizing all data before it enters the data layer. Teams can also architect event tracking so they never push PII client-side in the first place.
Self-hosting third-party dependencies
Many common web dependencies, like web fonts or JavaScript libraries, often load from third-party CDNs. Each of these requests can transmit the user’s IP address to the third party. For example, loading fonts directly from Google Fonts sends visitor IP addresses to Google. The solution is self-hosting Google Fonts for GDPR compliance and other similar assets. By serving these files from your own domain, you prevent unnecessary data sharing with external parties.
How do you integrate script orchestration with an enterprise CMP?
Correctly integrating an enterprise CMP like OneTrust with tag management systems is critical. A misconfiguration can nullify the entire purpose of the CMP, allowing trackers to fire without permission. Success depends on precise script sequencing and conditional logic.
Configuring tag managers for conditional execution
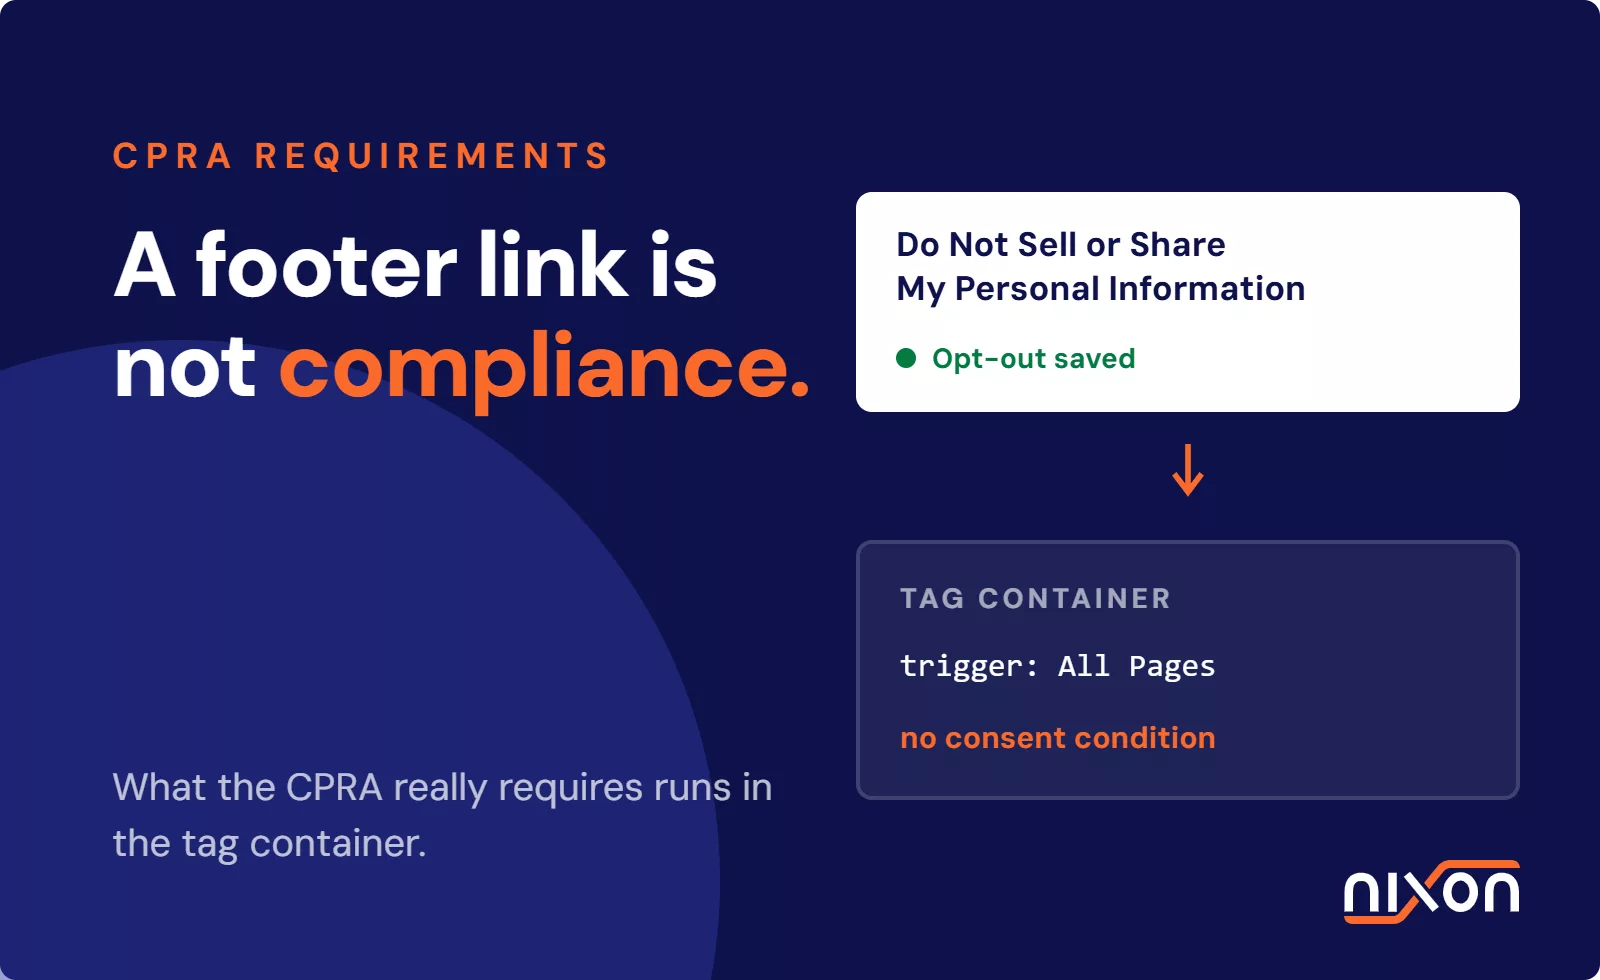
A tag management system, such as Google Tag Manager, must listen for consent signals from the CMP. This involves creating triggers based on the consent categories the user approved. For example, a Google Analytics tag should only fire if the CMP has broadcast an event indicating consent for “performance” or “analytics” cookies. A detailed OneTrust cookie consent setup checklist can guide developers. It helps them map these consent states to the correct tag manager triggers, ensuring no tag fires without the proper legal basis.
Eliminating race conditions between CMP and DOM loading
A frequent point of failure is a race condition where the tag manager script executes before the CMP determines the user’s consent status. To prevent this, the CMP script must load and initialize first. Developers often achieve this by placing it synchronously high in the <head> of the HTML document. They must ensure that no other tracking scripts load before the CMP has established the consent state. Other scripts can then check this state. After implementation, it is essential to validate your OneTrust consent implementation to confirm that scripts wait for the proper consent signals.
Auditing and maintaining technical compliance across web builds
Privacy by design is an ongoing process, not a one-time project. Development teams need workflows to audit and maintain compliance as the website evolves. This includes both manual checks and automated monitoring.
During development, engineers can use browser DevTools. They can inspect network requests on page load and ensure no unconsented trackers are firing. A good technical guide to tracker detection provides methods for identifying these data leaks. For larger organizations, manual checks do not scale. Automated scans can be integrated into CI/CD pipelines to catch regressions before they reach production. Continuous monitoring solutions, like Nixon Platform, address multi-brand website compliance risks. They automatically detect new third-party tags and consent gaps across complex website portfolios over time.
Privacy by design for websites is not accomplished by adding a cookie banner at the end of a project. It requires embedding consent logic into frontend architecture from day one. We often see teams struggle to translate these architectural patterns into a correctly configured CMP. If your engineering team needs to architect and audit a custom OneTrust implementation, our experts can provide OneTrust implementation support to ensure your technical setup meets regulatory expectations.
Frequently Asked Questions (FAQ)
What is privacy by design for websites?
Privacy by design for websites is an engineering approach that bakes data protection into a website's core architecture from the start. Instead of adding a consent banner as an afterthought, it means building systems that default to collecting no data. This aligns with GDPR Article 25, which requires technical measures to ensure user privacy is the default setting, not an option the user has to find.
How does privacy by design impact frontend web development?
It makes privacy a core development task, not just a legal requirement. Frontend developers must actively manage how and when third-party scripts load, ensuring they fire only after explicit user consent. This involves configuring tag managers with consent-based triggers, sanitizing data layers to prevent PII leakage, and self-hosting dependencies like fonts to avoid sharing user IP addresses with third parties.
Why do third-party marketing tags leak data before cookie consent?
This happens due to a technical race condition. Many marketing and analytics tags are designed to load asynchronously for performance reasons. This means they can execute and send data to their servers before the website's consent banner has fully loaded and registered the user's choice. As a result, data is collected without a legal basis, even if only for a few seconds.
How do developers prevent race conditions with consent management platforms?
Developers prevent race conditions by controlling script execution order. The Consent Management Platform (CMP) script must be loaded synchronously and placed as high as possible in the website's HTML `<head>`. This ensures it runs and establishes the user's consent status before any tag manager or analytics script can execute. All other tracking scripts are then configured to wait for a signal from the CMP before firing.
What is the difference between a privacy policy and privacy by design in code?
A privacy policy is a legal document that describes how an organization handles data. It is a statement of intent. Privacy by design is the technical implementation of that policy in the website's code. It's the difference between saying you respect consent and actually writing code that blocks a tracker from firing until consent is given. One is a promise, the other is the proof.